Website and server security
Protektac: know your websites and servers, harden them, prove it
Vulnerability assessments from the outside, attack analysis of your server logs, and a ranked PDF report that says what to fix first, in words a manager can follow.
What it is
Security findings people actually act on
Most scanners hand you hundreds of findings and no idea where to start. Protektac gives you a short, ranked list of what matters on this target, why it matters, and the exact steps to fix it.
Enter an address
A website address or an IP address is all it needs. Nothing to install and no login to share.
Look from outside
Protektac reads only what the internet can already see. No agent, no change to the site, no attack traffic.
Rank what it finds
Tested rules put every weakness in high, medium or low, with exploited flaws first.
Report and plan
A branded PDF with a plain summary and an ordered plan: fix now, fix next, plan.
Severity is decided by tested rules at every step. The AI only explains the findings and orders the plan.
01 / Vulnerability assessment
See what an attacker sees, then fix it
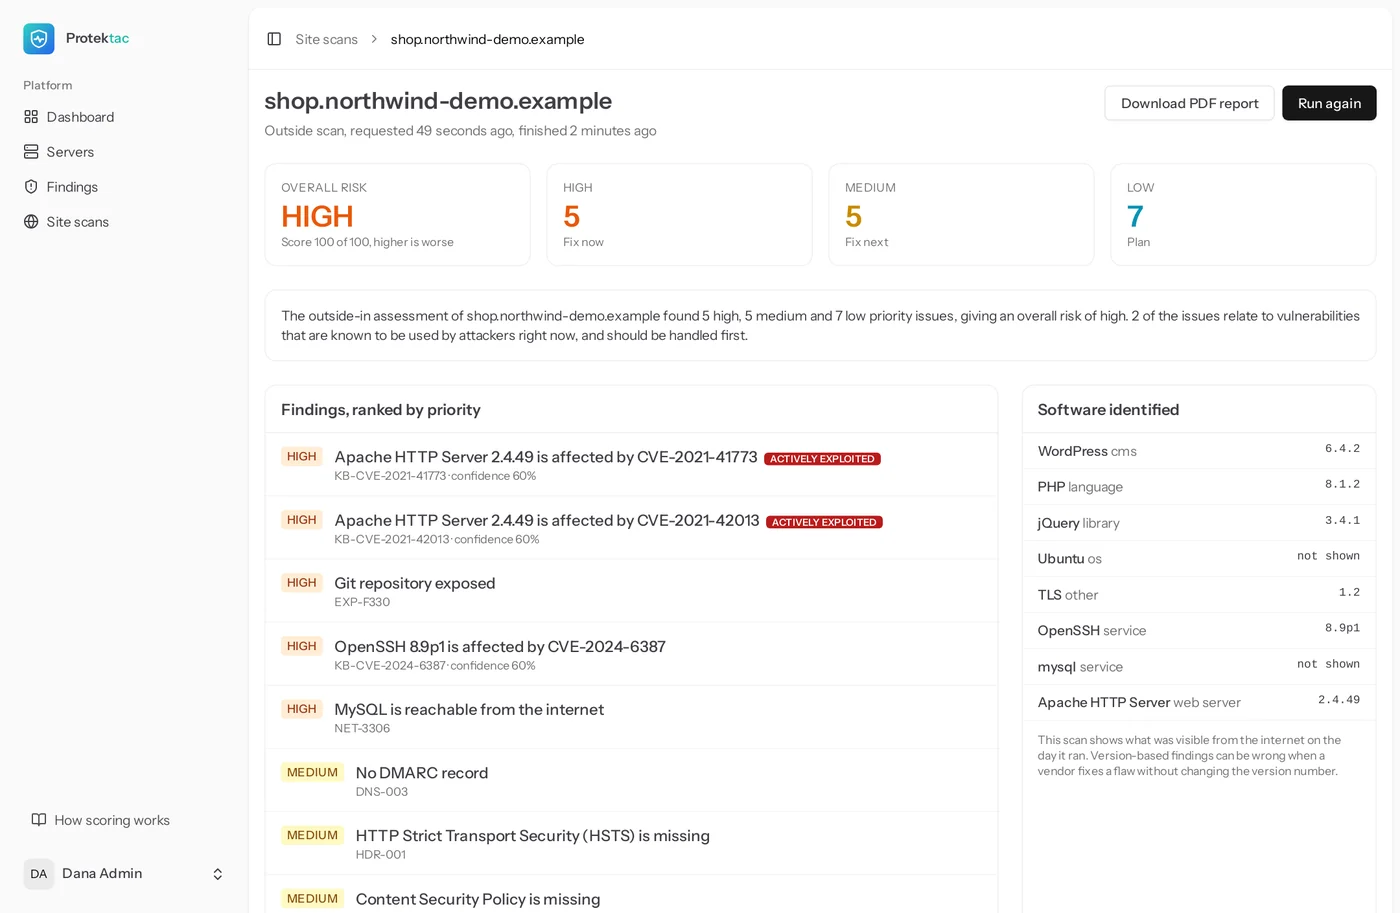
Enter a website address or an IP address in your dashboard. Protektac identifies the software behind it and lists every weakness it finds, ranked by how urgently each needs attention.
- Included
- Five scans a day for every subscriber, from your own dashboard
- Minutes
- From address to ranked findings and a PDF
- Nothing installed
- No login, no agent, no change to the site
- Read-only
- No attack traffic, no password guessing
High, medium or low
Decided by rules, not by guesswork
Inside the high band, findings tied to a vulnerability known to be exploited are marked as such and sorted first.
High. Fix now
Weaknesses attackers use today, or that expose data or control.
A database open to the internet. A web server with a known exploited flaw. An exposed code repository.
Medium. Fix next
Gaps that make an attack easier or more damaging.
No protection against forged email. A certificate about to expire. Missing HSTS.
Low. Plan
Hardening that lowers risk over time.
Missing browser headers. Version numbers shown to everyone. No CAA record.
What an outside assessment covers
Six areas, one ranked list
Software
The products and versions behind the site, and the known vulnerabilities for each.
Encryption
Certificate validity and trust, protocol and cipher strength.
Web
Security headers, cookie flags, redirects, and files that should never be public.
Network
Which common service ports answer, such as databases, remote desktop and SSH.
Email and DNS
SPF and DMARC against forged mail, CAA against mis-issued certificates.
Plan
An ordered action plan: fix now, fix next, plan, each step tied to a finding.
02 / The report
A branded PDF the owner can act on
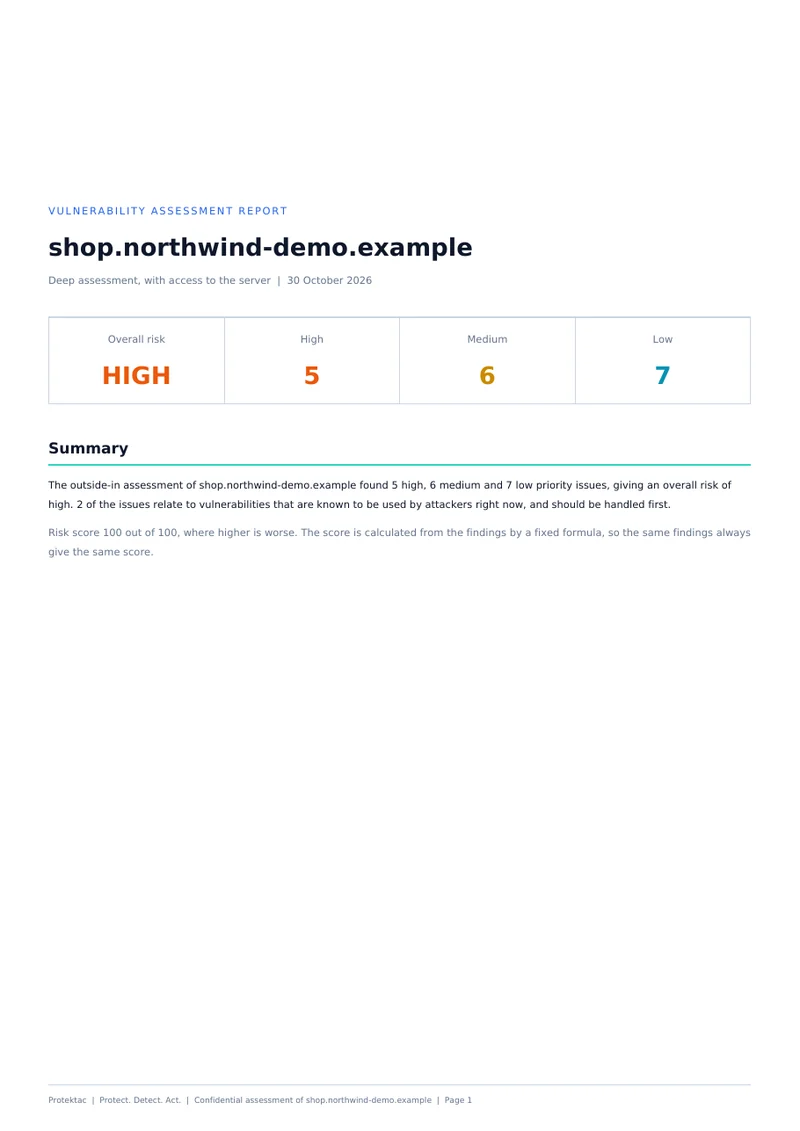
Hand it to whoever runs the server. Each finding says what was seen, what to do, and how confident we are. Exploited flaws carry a flag.
- Summary
- Overall risk, counts by band and a plain-language summary on page one
- Software
- What was found on the target, and how it was identified
- Findings
- Ranked, with what we saw and what to do
- Action plan
- Fix now, fix next, plan, each step tied to a finding
- Honest
- Version-based findings carry a lower confidence, and the report says why
- Limits
- What the assessment cannot see, stated on every report
03 / Attack analysis
Is someone attacking your server right now?
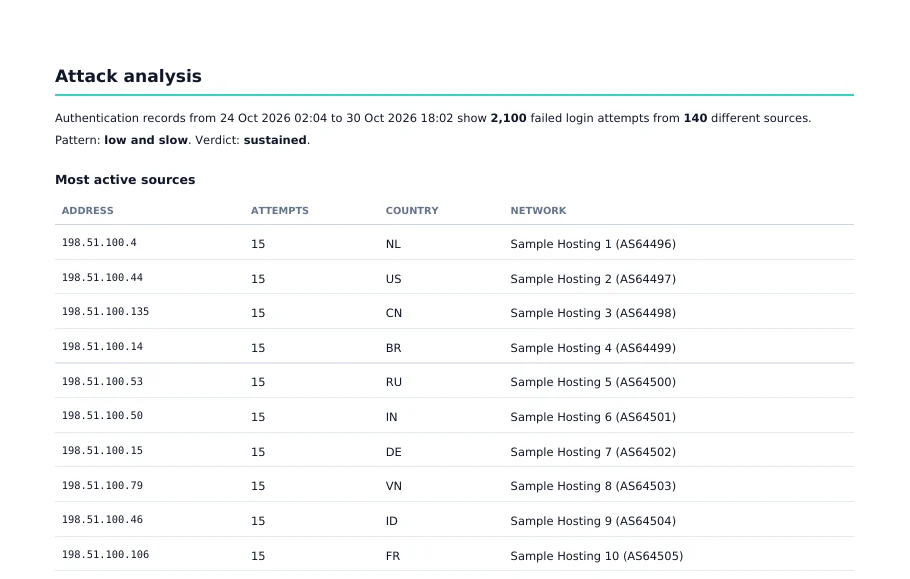
Share the server’s login log and the assessment goes inside. It shows whether the server is under a sustained password-guessing campaign, who is behind it and what they probably want.
- Verdict
- Background noise, a sustained campaign, or a likely compromise
- Motive
- Botnet scanning, leaked-password reuse, or pressure on one account, each with a confidence level
- Caveat
- Motive is an inference from the pattern of traffic, never a fact about who attacked
- Defences
- The ones that suit the pattern: key-only logins, automatic bans, or limiting who can reach SSH
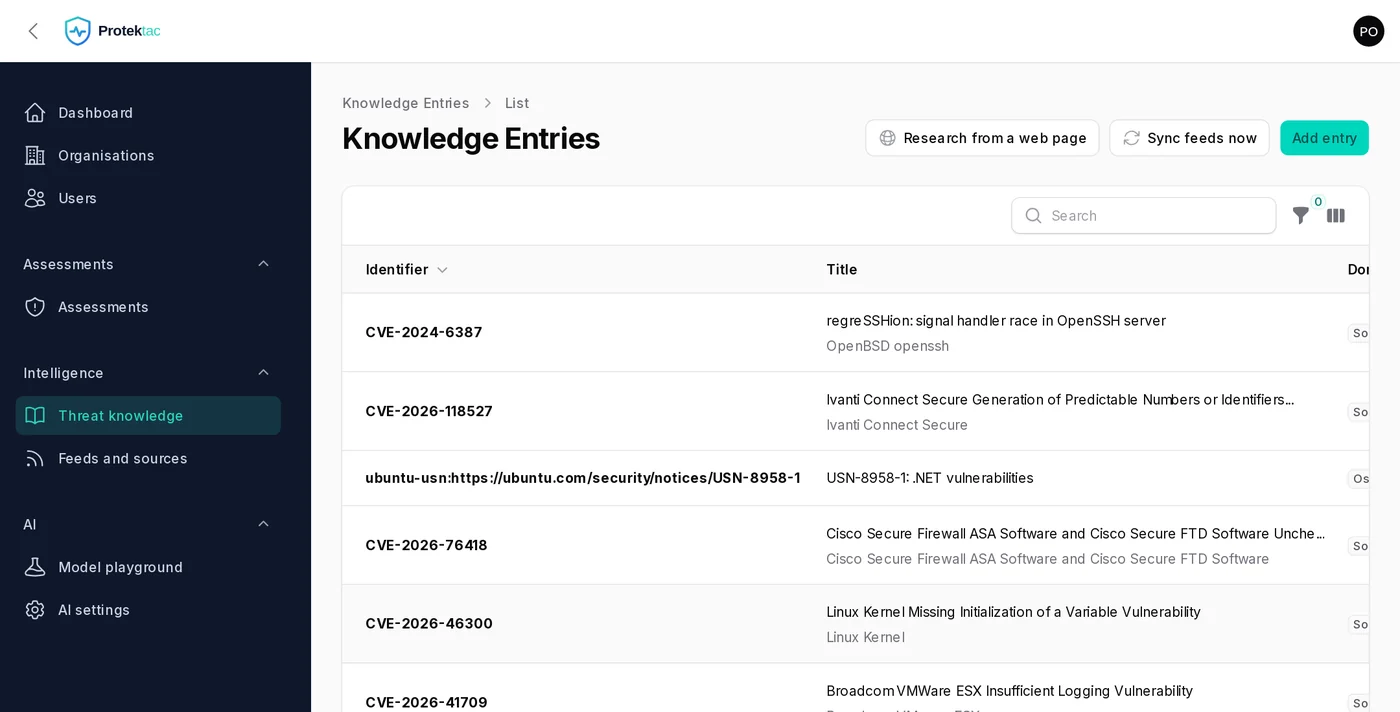
04 / Threat intelligence
A knowledge base that keeps itself current
Behind every assessment is a library covering software products, operating systems and programming languages. It updates itself every four hours from public sources, so a newly published or newly exploited flaw reaches your next scan within hours.
AI that is tested before it writes for you
Checked on the real tasks first
Reports use an AI model to explain findings and order the action plan. Before we trust a model with that job, we test it and score the answers automatically.
Explain
A vulnerability for a non-technical owner, without inventing CVE numbers.
Rank
A set of findings, scored against known answers.
Read
An attack pattern, with calibrated confidence and no overclaiming.
Resist
Instructions hidden inside the content it is summarising.
Never
Change a finding, its severity or the score.
Who it is for
For anyone who answers for a server
Agencies and hosts
Web agencies and hosting companies that look after sites and servers for clients, and need to show those clients proof.
Software companies
Teams whose buyers send security questionnaires and ask for evidence.
Service providers
Managed service providers with many customers and no security department.
Any business
Anyone who runs their own servers and has nobody with time to review them.
Built for trust
A security tool that is safe to install
Outside assessments install nothing. The agent for audits from inside your servers is in development, to these rules.
No credentials
The agent connects out from your server. There are no passwords or keys on our side to leak.
Signed
Everything the agent runs is signed with an offline key, so a breach of Protektac cannot push code to you.
Visible
The agent runs as a limited user, and you can read its exact command list before enrolling.
Explains, does not act
The AI explains findings. Tested code sets the score, and every command comes from a reviewed library.
Standards
CIS Benchmarks, CVSS, EPSS, CISA KEV and MITRE ATT&CK, with compliance packs planned.
Server audits, in development
Access, patching, exposure, integrity, hardening and logging, checked from inside each server.
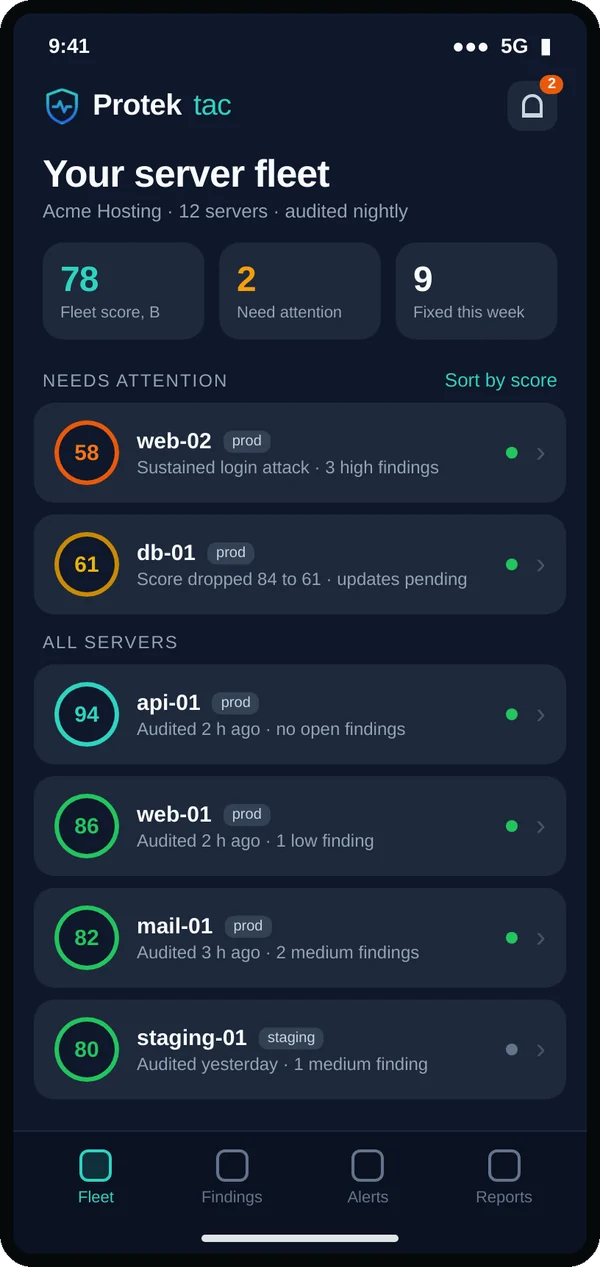
What is coming
From one website to your whole fleet
Now
Site scans from your own dashboard, ranked PDF reports, the threat knowledge base, login attack analysis and model testing, with design partners.
Next
The agent for Ubuntu and Debian, scheduled audits, the fleet dashboard, guided and automatic safe fixes, and Red Hat family support.
After that
Continuous watching, alerts to Slack, Teams, PagerDuty and email, and defence actions.
Planned
The Protektac app for Android and iPhone: every server with its score, worst first, and a push notification when a score drops, a new high finding appears or a login campaign starts.
Plans
Priced per server, per month
Site scans are included in every plan today. Server audits arrive with the agent. Ask about pilot pricing.
| Plan | Starter | Pro | Business | Enterprise |
|---|---|---|---|---|
| Servers | Up to 5 | Up to 25 | Up to 100 | Custom |
| Audits | Weekly | Daily | On demand | On demand |
| Site scans | 5 a day | 5 a day | 5 a day | Custom |
| Fixes | Guided | Guided and automatic | Plus two-person approval | Plus custom actions |
| Continuous watching | No | Yes | Yes | Yes |
| Standards | CIS Level 1 | CIS Level 1 and 2 | Plus compliance packs | Plus STIG and custom |
| History kept | 90 days | 1 year | 3 years | Custom |
| Team seats | 3 | 10 | Unlimited | Unlimited |
Protect. Detect. Act.
Start with one website. We run the first assessment and walk you through the report, finding by finding.
Request a demoEmail us Quick check that you are human: